Qoder Launches Qoder Security, Putting Three Layers of Security into the AI Coding Session
 Morikawa says LIV players face 'business decision' after Rahm exit
 Tenzing Norgay's son says Himalayas sending climate warning
 On your bike! Bottas opts for two wheels to reach Singapore GP
 Alcaraz, Sinner, Osaka commit to Australian Open '1 Point Slam'
 Dodgers beat Braves to advance in MLB playoffs, Rays oust Yankees
 'A sun as black as my lungs': how corruption crucified a polluted Albania city
 The British historian helping the French rediscover de Gaulle
 Dodgers beat Braves to advance, Guardians survive in MLB playoffs
 Latin American, Caribbean women top Nobel literature buzz
 US says Fiji-based Chinese official paid bribes for Beijing
 After botched US execution, Christa Pike was nearly taken off life support
 Guinea-Bissau junta urges military unit loyal to ex-president to disarm
 InterContinental Hotels Group PLC Announces Transaction in Own Shares - October 08
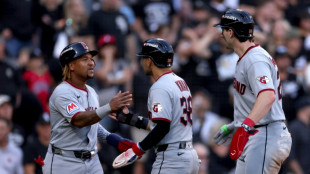 Guardians survive with 9-3 win over White Sox
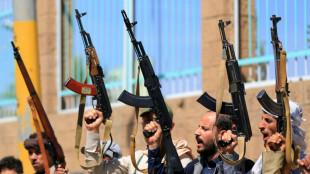 Saudi Arabia says 3 dead at airports after Houthis claim attacks
 Stocks slide as oil sees volatile trading day over Iran war fears
 Microsoft pushes AI vision with new, expensive Surface laptop
 Five children among 28 killed in Russian strikes on Ukraine
 Odell Beckham Jr signs with Minnesota Vikings
 Saudi Arabia says three dead at airports after Houthis claim attacks
 Trump plans to turn Florida golf course into presidential retreat
 WHO says cannot conduct full risk assessment on Russia plague reports
 After botched execution, US woman is awake and shackled to bed
 New Zealand fly-half Mo'unga ruled out of Australia Tests
 Protests in major Turkish city after mayor defects to Erdogan party
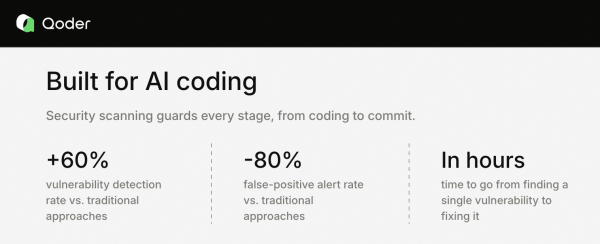
The built-in capability shifts code security from after-the-fact scanning to proactive, in-session protection, improving vulnerability detection by about 60 percent and cutting false-positive alerts by about 80 percent compared with traditional solutions
SINGAPORE, SG / ACCESS Newswire / July 23, 2026 / Qoder, the agentic coding platform with more than 5 million registered users, today announced Qoder Security, a built-in capability that embeds security review directly into the AI coding session. As code is written, Qoder Security runs three progressive layers of protection and fixes the issues it finds in the same session, before the code is committed.
The launch targets a widening gap between how fast Agent writes code and how slowly that code gets checked. Agent now assists in generating a large share of new code, and a July 2026 academic study that applied multi-tier verification to nearly 9,000 C++ programs found that AI-generated code triggers confirmed runtime violations at roughly twice the rate of human-written code, even after controlling for code length and test pass rates. Most security tooling, however, still runs after the fact, in CI pipelines or pre-release audits, when the developer's context is gone and fixes are slowest and most expensive.
"The speed of agentic coding has quietly become the speed at which vulnerabilities enter the repository," said Ding Yu, Head of Product at Qoder. "We believe security cannot depend on a model's good behavior. It has to be built into the product architecture. Qoder Security gives every developer the equivalent of a dedicated security engineer, one that reviews, verifies and fixes issues while the code is being written, not weeks later in a report."
From Static Scanning to Proactive Security
Traditional code security relies on rules and pattern matching. That approach catches hardcoded secrets and known dangerous calls, but it cannot reason about logic flaws such as authorization bypasses or exploitable data flows. Qoder Security, built on Qoder's proprietary security LLM, takes an approach the company calls proactive security. The system understands code context and taint propagation paths, verifies that a detected issue is actually reachable before reporting it, and then drives the fix itself.
The architecture separates the agent that writes code from the agent that reviews it, avoiding what engineers call reviewing its own work. On the review side, scanning and verification are split between two cooperating agents to improve accuracy. Once a fix lands, the next scan re-verifies it, closing the loop so no security debt is left behind.
Three Layers, Escalating Depth
Running a frontier-scale model over every line of code would be too slow and too expensive. Qoder Security instead assigns a distinct job to each of three layers:
Static Check. Pattern-based screening at generation time. Dangerous function calls and other known high-risk patterns are caught and fixed the moment they appear, with no latency and no model cost.
Lightweight Scan. After a coding task wraps up, the system suggests a semantic review of the incremental changes. This layer reasons about what the code is trying to do, catching risks such as SQL injection, remote command execution and sensitive data exposure, and verifies reachability before reporting.
Deep Scan. Before code is pushed, the system offers a cross-file, cross-function analysis that traces complete data flows from taint source to dangerous sink, surfacing chained vulnerabilities invisible from any single file.
None of the layers interrupts the developer. The first runs silently; the other two appear as suggestions at natural break points in the workflow and run only when the developer says yes. A scan can also be triggered at any time with the /security-scan command or a plain-language request.
Reported Results
According to company data, Qoder Security improves vulnerability detection rates by about 60 percent and reduces false-positive alerts by about 80 percent compared with traditional solutions, shrinking the time from discovery to fix from days to minutes. In internal testing ahead of launch, the system surfaced more than 600 security issues across production-grade open-source projects and AI infrastructure components, many of them widely used and actively maintained. Within Qoder's own engineering organization, security-related comments in code review have dropped by roughly 35 to 45 percent since adoption.
The broader industry is converging on the same conclusion. Leading AI labs have begun building security review into their coding tools, some at the repository level, others inside the coding session. Qoder Security productizes the in-session approach end to end, with three layers of protection, same-session remediation and closed-loop re-verification available out of the box.
Qoder Security is designed to complement existing security programs rather than replace them. CI-stage scanning and human review remain the right tools for compliance and organizational control; Qoder Security shifts detection and remediation left, to the moment the code is born. Findings may still include false positives, and developers always decide whether to accept a fix.
Availability
Qoder Security is available now in Qoder Desktop and in Qoder CLI. It requires no plugins and no configuration files: open Settings > Security in Qoder Desktop, or run /security-settings in the CLI, and switch it on. Static Check is free; Lightweight Scan and Deep Scan consume credits.
About Qoder
Qoder is an agentic coding platform serving more than 5 million registered developers worldwide through Qoder Desktop, Qoder CLI and JetBrains plugin. Launched in 2025, Qoder pairs autonomous coding agents to help developers ship reliable software faster. Learn more at qoder.com.
Media Contact
Organization: Qoder
Contact Person Name: Nathan Steel
Website: https://qoder.com
Email: [email protected]
City: Singapore
Country: Singapore
SOURCE: Qoder
View the original press release on ACCESS Newswire
L.Davis--AMWN