-
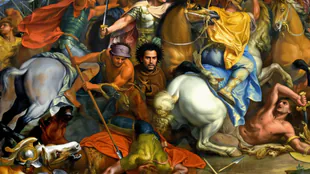 Edmund Richardson Wins Baillie Gifford Prize for 'Alexander' Biography
-
Pakistan Demands Grant-Based Climate Finance at COP31 to Avoid Debt Trap
-
 BYD Drops Rotating Screens in New Models Due to Tech Limits
-
E Pellicci Pop-Up at Selfridges Brings Back Nostalgic School Cake
-
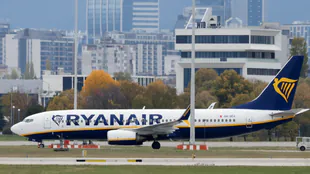 Ryanair Flight from Rome Makes Emergency Landing in Lisbon After Bomb Threat
-
Coronation Street's Debbie Webster Steps Down as Dementia Storyline Intensifies
-
 Maltese President Visits London Hospital to Support Families Facing Medical Care Challenges
PRIVACY POLICY
PRIVACY POLICY OF "AMERICAN MARCONI WIRELESS NEWS"
Controller and privacy contact
SCANDIC TRUST GROUP LLC is responsible for the processing of personal data described in this Privacy Policy where it determines the purposes and means of that processing. References to "we", "us" and "our" mean SCANDIC TRUST GROUP LLC in its capacity as the publisher and service provider of "AMERICAN MARCONI WIRELESS NEWS".
SCANDIC TRUST GROUP LLC
IQ Business Centre
Bolsunovska Street 13–15
01014 Kyiv / Ukraine
Email: [email protected]
Legal form: limited liability company incorporated under Ukrainian law, LLC.
Registration number: 1010351020000018952.
The address above is our operational and correspondence address. Privacy inquiries, complaints and requests to exercise your rights may be sent to this address or to the email address above. The registration number identifies the Ukrainian company. "AMERICAN MARCONI WIRELESS NEWS" is the publication’s title and does not constitute a separate legal entity.
Registered office and company address
SCANDIC TRUST GROUP LLC
Oksamytova Street 1-b, Office 30
Sofiivska Borshchahivka
Kyiv Region - 08147 / Ukraine
Technical operation and administration
SCANDIC ASSETS FZCO
Dubai Silicon Oasis DDP
Building A1/A2
Dubai - 342001 / United Arab Emirates
Telephone: +971 54 221 5217.
SCANDIC ASSETS FZCO provides technical services within the scope of its appointment. Where it processes personal data on behalf of SCANDIC TRUST GROUP LLC, access must be limited to the information and functions necessary for the assigned services. Processing subject to the New Jersey Data Privacy Law must comply with the applicable controller–processor requirements, including N.J.S.A. 56:8-166.16. The parties’ respective responsibilities depend on their actual activities and decisions. Technical involvement or membership of the same corporate group does not, by itself, determine whether an organization acts as a controller or processor.
Commercial cooperation
LEGIER Beteiligungs mbH
Kurfürstendamm 14
10719 Berlin
Federal Republic of Germany
Commercial register: HRB 57837
Register court: Amtsgericht Charlottenburg, Berlin
VAT identification number: DE413445833
Telephone: +49 30 99211 3469
Fax: +49 30 99211 3225
Email: [email protected]
Where LEGIER Beteiligungs mbH participates in an advertising inquiry or commercial arrangement, personal data may be disclosed to it for the specified purpose and to the extent necessary for its role. Commercial cooperation does not provide unrestricted access to reader, subscriber or confidential editorial information. Where that company determines its own purposes and means of processing, its responsibilities and the relevant privacy information must be identified in connection with the particular activity.
Introduction and scope
This Privacy Policy explains how personal data is handled in connection with the websites, applications, editorial activities and other services of "AMERICAN MARCONI WIRELESS NEWS". It describes the categories of information concerned, the purposes of processing, recipients, international processing, retention, privacy choices and available rights. Provisions concerning accounts, subscriptions, orders, newsletters, comments, events and other additional functions apply where those functions are provided. Sections concerning external technologies apply to the services and configurations in which those technologies are used. Information supplied when a particular service collects personal data supplements this Policy. Reading or accepting this Policy does not constitute consent to advertising, sensitive-data processing or another activity for which a separate choice is required. Statutory privacy rights do not depend on acceptance of the Terms of Service.
Applicable United States and New Jersey law
The principal state framework addressed by this Policy is the New Jersey Data Privacy Law, N.J.S.A. 56:8-166.4 et seq., including the amendments introduced by P.L. 2026, c.25. Its general coverage depends on the statutory territorial requirements, processing thresholds and exceptions. These include conducting business in New Jersey or targeting products or services to its residents and, during a calendar year, processing the personal data of at least 100,000 consumers, excluding data processed solely to complete payment transactions, or processing the data of at least 25,000 consumers while deriving revenue or receiving a discount from its sale. The sensitive-data sales prohibition introduced in 2026 has a broader numerical scope, as explained below. Relevant federal protections include the Federal Trade Commission Act, the Children’s Online Privacy Protection Act, the Video Privacy Protection Act and applicable communications-privacy legislation. New Jersey consumer-protection, confidentiality, secure-disposal and breach-notification requirements also apply within their respective scope. Constitutional protections for freedom of speech and the press remain relevant to journalistic publication.
A) General information on personal data processing
Personal data generally means information linked or reasonably linkable to an identified or identifiable individual. Depending on the activity, it may include names, contact details, account identifiers, correspondence, subscription and transaction records, contributions, photographs, recordings, IP addresses, device information, preferences and information about use of the services. Different statutes may define protected information differently. Under the New Jersey Data Privacy Law, qualifying de-identified data and publicly available information are excluded from the definition of personal data. Those exclusions must satisfy the statutory definitions. Removing a name, replacing an identifier or combining information into a dataset does not necessarily make it de-identified. Where we maintain information as de-identified data, it must remain subject to the required safeguards against re-identification and inappropriate onward use. Collection and use must be limited to information reasonably necessary for disclosed and lawful purposes.
Purposes and conditions of processing
The purposes depend on the service and the circumstances in which information is received. Relevant activities include:
- Providing requested services: delivering content, administering an account or subscription, processing an order and responding to service requests.
- Communications: answering correspondence, handling complaints and communicating information necessary for an existing service or transaction.
- Payments and administration: recording transactions, reconciling payments, maintaining required business records and addressing billing disputes.
- Security and fraud prevention: protecting accounts, maintaining service integrity, investigating technical incidents and addressing unlawful or abusive activity.
- Journalism and publication: preparing, publishing, correcting and maintaining news, commentary, images, recordings and editorial archives, subject to applicable legal protections and restrictions.
- Service analysis and improvement: evaluating functionality, performance and use within the limits described in this Policy and any applicable privacy choices.
- Optional communications and advertising: providing requested newsletters or other optional functions and carrying out advertising-related processing where the applicable disclosure, consent and opt-out requirements are satisfied.
- Legal obligations and claims: complying with applicable requirements, responding to valid legal process and establishing, exercising or defending legal claims.
A disclosed purpose does not authorize unlimited collection or every possible use of the information. Where the law requires consent, processing must remain within the specific consent given. Necessary account administration must remain distinguishable from optional advertising and unrelated profiling.
Processing required or permitted by law
Applicable law may permit processing necessary to perform a requested service, comply with a legal obligation, address fraud or security incidents, protect life or physical safety, or establish and defend legal claims. These permissions are limited by their conditions and do not authorize unrelated commercial use. Under the New Jersey Data Privacy Law, processing for a purpose that is neither reasonably necessary to nor compatible with the disclosed purpose generally requires the consumer’s consent unless a statutory exception applies. Any exception relied upon must remain limited to necessary, reasonable and proportionate processing for the permitted purpose. Consent cannot authorize an activity that the law prohibits, including a sensitive-data sale covered by New Jersey’s statutory prohibition.
Sources of personal data and information provided to you
Information may be supplied directly by you, generated through the technical operation of a service, provided by a person authorized to act for you, or received from service providers involved in a requested transaction. Editorial information may come from interviews, contributors, news services, public records, published material and other lawful sources relevant to reporting. Information received from another organization must be used consistently with its lawful source, the purpose for which it was obtained and any applicable restrictions. Information made available to a limited audience is not automatically public information. Notices supplied with forms, accounts, subscriptions and other collection points must explain the relevant processing in a reasonably accessible and meaningful manner. This Policy does not authorize the collection of unrelated information merely because it can be found online.
Editorial and journalistic processing
Personal information may form part of news reporting, commentary, photographs, audiovisual material and editorial archives. Applicable protections include the First Amendment to the United States Constitution, Article I, paragraph 6 of the New Jersey Constitution and relevant rules concerning privacy, defamation, confidentiality and evidentiary privilege. The legal treatment depends on the information, how it was obtained, the nature of the publication and the rights involved. Constitutional protection for truthful reporting on matters of public concern does not create a general license to unlawfully obtain information or publish every private detail. Similarly, the operation of a newspaper does not automatically exempt subscriber administration, advertising, audience measurement or other commercial processing from applicable privacy requirements. Editorial publication and commercial reader-data processing must be assessed according to their respective functions.
Privacy, confidential sources and editorial archives
Confidential sources, unpublished submissions and other protected editorial information require appropriate confidentiality and access controls. New Jersey’s newsperson’s privilege, N.J.S.A. 2A:84A-21 et seq., may protect qualifying sources and information when its requirements are satisfied. The federal Privacy Protection Act of 1980 provides additional protections concerning certain government searches and seizures of journalistic work product and documentary material, subject to its exceptions. These protections do not amount to an absolute promise of immunity from every lawful disclosure requirement. Editorial archives may serve a continuing informational and historical purpose. A request concerning an archived article must be assessed in its context; neither automatic removal of lawful reporting nor indefinite retention of every underlying personal record follows merely from describing material as archival. The treatment of published material is addressed further in section I.
External platforms and distribution services
Where content is distributed through social networks, video or audio platforms, applications, connected televisions or voice services, the platform operator may process information for its own purposes. Depending on the service offered, this may involve platforms operated by X, Meta, Google, Apple, Amazon, Telegram, TikTok, Roku, Huawei, Spotify or other providers. A normal external link, an embedded player and an externally loaded image can produce different disclosures. An embedded resource may contact its provider when a page loads, before the visitor interacts with it. Being signed in to a platform may allow that provider to associate the interaction with an account. A platform account or acceptance of its terms does not establish unrestricted consent to disclosures from our services. Responsibility for processing that we determine or initiate remains governed by applicable law.
Technical information and voice services
Requests to access content may generate technical records. Depending on the service, device and connection, these may contain:
- The requested page, file or resource and the date and time of access.
- Response status, transferred data volume and technical error information.
- The IP address and available browser, operating-system or device information.
- Referring-page information where transmitted by the browser or platform.
- Connection information and identifiers necessary for delivery, security or the requested function.
These records support the purposes described in section E. Their collection does not authorize unrelated advertising profiles. Providers of voice services may process commands, recordings, transcripts and interaction records according to their own functions and settings. Requesting our content through such a service does not necessarily mean that we receive the original recording or the user’s complete interaction with that provider.
Sensitive data and information requiring additional protection
Under the New Jersey Data Privacy Law, sensitive data includes specified information concerning racial or ethnic origin, religious beliefs, health, qualifying financial-account credentials, sex life or sexual orientation, citizenship or immigration status, transgender or nonbinary status, genetic or qualifying biometric information, precise geolocation and personal data collected from a known child. Covered processing ordinarily requires prior consent, while processing information concerning a known child must comply with the applicable COPPA requirements. P.L. 2026, c.25 prohibits covered sales of sensitive data regardless of the number of consumers whose information the individual or entity controls or processes. The statutory definitions and exceptions remain relevant, and consent does not override that prohibition. Ordinary photographs and recordings are not automatically biometric identifiers; using them to identify a particular person can change the legal analysis. Criminal allegations, private communications and confidential submissions may require additional protection even where they do not fall within a particular statutory definition of sensitive data.
B) Contacting us
When you contact us by email, telephone or an available contact form, we process the information reasonably necessary to understand and respond to your inquiry. This may include your name, contact details, the content of your message and records of the response. The purpose may be ordinary correspondence, administration of a requested service, a contractual matter, a privacy request or an editorial submission. Please provide information relevant to the matter and avoid sending unnecessary identity documents, passwords or payment credentials. Where essential information is missing, we may request clarification sufficient to address the inquiry. Contacting us does not subscribe you to unrelated advertising. Correspondence is retained while the matter is being handled and thereafter according to section H and any applicable legal requirement.
C) Reservations, orders, subscriptions and user accounts
Where these services are offered, we process the identification, contact, account, contractual, order and payment information needed to provide them. Account information may include credentials, preferences, subscription status and records of account administration. Required fields and the consequences of not providing necessary information must be explained at the point of collection. Optional information and marketing choices must remain distinguishable from information needed for the service. Payment providers may process information independently for payment execution, authentication, fraud prevention or regulatory obligations. Their involvement does not necessarily give us access to full card or bank-account credentials. Information needed for billing must not be repurposed for unrelated sensitive profiling without satisfying the applicable legal requirements. Account closure, subscription cancellation and deletion of personal data are distinct matters; a request addressing more than one of them will be handled accordingly.
D) Accounting and statutory record retention
Financial and transaction records are retained for the period required by the law applicable to the company, transaction and record concerned. Where United States federal tax-record requirements apply, section 6001 of the Internal Revenue Code and its implementing regulations require relevant records to remain available for as long as their contents may be material to tax administration. Where New Jersey sales-and-use-tax record requirements apply, N.J.S.A. 54:32B-16 generally requires relevant records to be preserved for four years, subject to applicable extensions and other requirements. These rules do not establish a universal retention period for every category of reader information or every overseas company. A specific legal obligation or legal hold may require longer preservation of relevant records. Records retained for accounting, tax or legal purposes must remain restricted to those purposes and must not be retained for unrelated marketing merely because their preservation is required.
E) Technical provision of the website and operational security
Technical information is processed to deliver requested content, maintain functionality, investigate faults and protect the services against unauthorized access, attacks and misuse. This can include server requests, authentication records, error information and security-related events. Collection must be proportionate to the operational purpose, and access must be restricted to persons and suppliers whose work requires it. Technical delivery and security processing must remain distinguishable from optional audience profiling or advertising. A security purpose does not authorize indefinite retention or unrestricted disclosure of browsing information. Routine records are retained for the period justified by their purpose, subject to section H. Relevant evidence of a specific incident may be preserved separately while necessary for the incident response or associated legal matter.
Cloudflare and cdnjs
Where Cloudflare services are used for content delivery, network protection or distribution of technical resources through cdnjs, the provider may receive IP addresses, request times, requested-resource details and technical information transmitted by the browser. The information and purposes depend on the particular service and configuration. Processing needed to deliver or secure a requested resource must be distinguished from separate analytics or advertising activities. Browser caching of a technical file is different from retention of request information in server records. The use of a content delivery network does not itself authorize every associated use or disclosure of personal data. The relevant processing role, contractual restrictions and international access arrangements are addressed in section G.
Google Fonts and externally loaded resources
Where fonts or other resources are loaded directly from Google or another external provider, the browser may disclose its IP address, the requested resource and associated technical information to that provider. The absence of cookies does not necessarily mean that no personal data is processed. The purposes, recipients and applicable privacy requirements depend on the actual connection and any additional use of the information. Serving a font file locally avoids the separate browser request to the external font provider for that file. Technical resource delivery must not be described as anonymous solely because the resource is a font, image, script or style file.
F) Cookies, device access and tracking technologies
Cookies and similar technologies can store information on a device or access information already stored there. Related technologies include browser storage, tracking pixels, software identifiers and device fingerprinting. Their legal treatment depends on the information involved, the purposes, the recipients and the applicable law. New Jersey law does not establish a universal requirement for prior consent to every cookie. It does impose requirements concerning sensitive information, certain processing involving minors, purpose limitations, qualifying sales, targeted advertising and other covered activities. Federal and state communications-privacy rules and the Video Privacy Protection Act may impose additional requirements in particular circumstances. Descriptions such as "cookieless", "statistics", "personalization" or "security" do not, by themselves, determine whether an operation is lawful or whether a privacy choice is required.
Consent and statutory requirements
Where consent is required, it must be obtained before the relevant processing begins and must represent a freely given, specific, informed and unambiguous affirmative choice. Acceptance of a general privacy policy or terms of use is not a substitute for that choice. Consent obtained through misleading or manipulative design is not valid under the New Jersey Data Privacy Law. Processing that is permitted without prior consent must still satisfy applicable notice, purpose-limitation, security and opt-out requirements. Any recording or interception of communications must comply with the relevant federal and state rules; a general reference to analytics does not provide blanket authorization. A statutory prohibition remains binding even if an individual is willing to consent.
Statistics used to improve our services
Statistical analysis may be used to understand page performance, detect technical problems and evaluate use of the services. The information collected must be proportionate to the stated purpose. Aggregated reporting must be distinguished from maintaining identifiable histories or combining activity across unrelated services. Where information is treated as de-identified, the applicable safeguards against linking it back to a person or device must be satisfied. Describing processing as service improvement does not remove a right to opt out where the activity also constitutes a sale, targeted advertising or another activity covered by an opt-out right. A supplier engaged to produce statistics must not receive unrestricted permission to use identifiable information for unrelated purposes.
Your choices and withdrawal of consent
Privacy choices may be communicated through the relevant controls made available with a service or by emailing [email protected]. Where processing depends on consent, withdrawal must be as easy as giving consent. Under the applicable New Jersey consent-withdrawal provision, processing based on that consent must cease as soon as practicable and no later than 15 days after receipt of the request. This does not remove a separate lawful obligation to retain particular records or the need to retain a limited record of the choice. Qualifying opt-outs from sales and targeted advertising must also be honored, including qualifying universal opt-out signals such as Global Privacy Control where the statutory requirements apply. Browser settings can block or delete cookies, but deletion of a cookie does not necessarily communicate withdrawal or an opt-out to every recipient. Silence, continued browsing or an unrelated account action does not reverse an existing privacy choice.
Remembering cookie and language choices
Under this Policy, our own record used to remember a cookie or consent choice is retained for no longer than 12 months from the last active choice, subject to the limited compliance and suppression records described in section H. Where a cookie named "laravel_cookie_consent" is used for this purpose, its function must remain limited to remembering the relevant choice. A language preference, including a session cookie named "language" where used, is retained for the session or, where a persistent preference is requested, for the necessary period up to 12 months. Browser session restoration may affect the practical lifetime of a session cookie. These are policy limits rather than a claim that New Jersey law prescribes a universal 12-month cookie period. A return visit does not, by itself, create new consent or cancel an opt-out.
Cloudflare Web Analytics
Where Cloudflare Web Analytics is used, the service may process page-view, performance, referring-page and browser or device information according to its configuration. Cloudflare describes this product as operating without tracking individual users across its customers’ websites. The actual implementation must nevertheless be assessed against applicable privacy requirements and the choices made by users. Cloudflare’s product documentation describes retention of unsampled beacon data for seven days, followed by sampling or aggregation, and access to reports covering the preceding six months. Sampling does not itself establish that information meets a legal definition of de-identified data. These product descriptions do not determine the retention periods or processing purposes of every other Cloudflare service.
Advertising, personalization and measurement purposes
Where the relevant functions are provided, separately explained purposes may include:
- Selecting advertising using limited information.
- Creating profiles for personalized advertising.
- Using profiles to select personalized advertising.
- Creating profiles to personalize content.
- Using profiles to select personalized content.
- Measuring advertising performance.
- Measuring content use and performance.
- Analyzing audiences using statistics or information from different sources.
- Developing and improving services.
- Selecting content using limited information.
The applicable notice must identify the processing actually involved and the available choices. Under New Jersey law, targeted advertising generally concerns advertising selected using information about activity over time and across nonaffiliated websites or applications. Contextual advertising and specified activities confined to a controller’s own services are treated differently under that definition. A sale may involve monetary or other valuable consideration and is not limited to exchanging a list for cash; statutory exclusions remain relevant. An advertising arrangement must be assessed according to its substance. Industry terminology or participation in an advertising framework does not replace legal requirements. Sensitive information and information concerning minors remain subject to their additional protections.
G) Recipients and international processing
Personal data is disclosed for identified lawful purposes and only to the extent justified by the relevant activity. Recipients may include technical suppliers, providers involved in a requested transaction, professional advisers, relevant editorial contributors and competent authorities or courts where disclosure is lawful. Information disclosed must correspond to the recipient’s actual role. A technical supplier may need request information or account identifiers; a payment provider may need transaction and billing information; an adviser may need records concerning a particular legal or accounting matter. A commercial relationship does not itself authorize access to all information held by the publication. Where the New Jersey controller–processor requirements apply, the processing contract must address instructions, confidentiality, security, duration, deletion or return, subcontractors and compliance assistance. An organization that independently determines purposes and means may have controller responsibilities for that processing.
Principal organizations and service-related recipients
Relevant organizations and recipient categories include:
- SCANDIC TRUST GROUP LLC, Ukraine: controller for the activities described in this Policy for which it determines the purposes and means of processing.
- SCANDIC ASSETS FZCO, United Arab Emirates: technical operation and administration, with access limited to the information required for its assigned services.
- LEGIER Beteiligungs mbH, Germany: commercial inquiries and arrangements in which it participates, limited to relevant business-contact and transaction information.
- Cloudflare, Inc., United States: technical request, delivery, security or analytics information where the relevant Cloudflare services are used.
- The relevant Google service provider: technical and interaction information where Google-hosted resources, YouTube or other Google services are used; the responsible entity and role depend on the service.
- Payment, communication, delivery and other service providers: information necessary for an actual transaction, requested communication or service, with relevant details supplied in connection with that activity.
- Professional advisers, auditors, courts and competent authorities: information necessary for the specific advice, obligation, proceeding or lawful request.
- Editorial contributors and distribution partners: information necessary for the relevant editorial activity or authorized distribution, subject to confidentiality, applicable rights and legal restrictions.
Information supplied about recipients must reflect actual disclosures. A provider’s use of information for its own purposes must not be presented as processing performed solely under our instructions.
Overseas processing and remote access
The controller is established in Ukraine, the technical company is established in the United Arab Emirates and the commercial cooperation company is established in Germany. Processing may therefore involve those countries and other locations used by the relevant service providers, including the United States. Remote access by an overseas organization can expose information to that organization even where the server remains in another country. Applicable privacy and security obligations continue to govern the processing. A company’s address alone does not establish where every record is stored, which persons can access it or whether a particular disclosure is lawful. International access must remain limited to the relevant service, authority and purpose.
Safeguards for international processing
Safeguards must be appropriate to the information, the recipient’s role and the risks of the processing. They may include contractual purpose restrictions, confidentiality requirements, access controls, secure transmission, appropriate encryption, limits on onward disclosure and arrangements for deletion, return and incident reporting. Where a recipient acts as a processor, the applicable processing requirements remain binding regardless of its location. Where it acts independently, its own purposes and responsibilities must be identified. A general reference to international operations does not provide consent to an otherwise restricted disclosure. Information about relevant recipients and processing arrangements may be requested through the privacy contact, subject to the protection of confidential information and other lawful limitations.
Restrictions concerning sensitive cross-border disclosures
Certain cross-border transactions are subject to additional federal restrictions. The Protecting Americans’ Data from Foreign Adversaries Act of 2024 restricts covered data brokers from making specified sensitive information about United States individuals available to foreign adversaries or entities controlled by them, subject to its definitions and exclusions. The Department of Justice’s Data Security Program, implemented through 28 C.F.R. Part 202, separately prohibits or restricts certain transactions involving United States government-related data or Americans’ bulk sensitive personal data and covered foreign recipients. These regimes have distinct scope, exceptions and requirements. Ordinary technical outsourcing, journalistic publication and a covered data-broker transaction must not be treated as interchangeable. An individual’s acceptance of this Policy cannot waive a statutory prohibition.
H) Retention and deletion of personal data
Under this Policy, the ordinary maximum for our own routine operational records is 12 months from the event specified below. Information is deleted or appropriately de-identified earlier where it is no longer necessary. Longer retention is limited to information needed for a continuing service, a specific legal obligation, legal claims, continued respect for a privacy choice or a lawful editorial purpose. A maximum period does not justify retaining unnecessary information until that period expires.
- Inquiries and correspondence: while the matter is being handled and ordinarily no longer than 12 months after closure, subject to necessary legal or evidential retention.
- Accounts and contracts: while needed for an active account or continuing agreement, followed by retention of necessary remaining records for ordinarily no longer than 12 months after closure or termination, except where accounting, legal or claims requirements justify longer retention.
- Technical and security records: for the period justified by their operational purpose and ordinarily no longer than 12 months from recording; relevant evidence of a specific incident may be retained separately while necessary.
- Cookie and preference records: ordinarily no longer than 12 months from the last active choice, with shorter periods appropriate to the function.
- Consent and privacy-request records: while necessary to implement and demonstrate the relevant choice or response, followed by limited retention for compliance or legal purposes where justified.
- Marketing suppression and opt-out records: the minimum information necessary to continue respecting the choice and prevent unwanted processing, without using that record to resume marketing.
- Accounting and tax records: for the period required by the applicable provisions described in section D.
- Journalistic material and archives: for the period justified by the editorial purpose, applicable rights, source protection and any relevant legal obligation.
- Information processed independently by external providers: according to the actual service, role and applicable law; our ordinary 12-month limit does not establish those providers’ independent retention periods or extend a shorter legal requirement.
Deletion must also be reflected in backup management. Information temporarily remaining in protected backups must not remain available for ordinary use and must be removed through the applicable replacement or deletion cycle. Restoring a backup must not permanently reverse a deletion or privacy choice. A legal hold must be limited to relevant information and end when preservation is no longer required. Where the Video Privacy Protection Act applies, its specific destruction requirements also govern covered records.
I) Your rights
Where the New Jersey Data Privacy Law applies, you have the following rights, subject to its conditions and exceptions:
- Information: to receive a reasonably accessible and meaningful notice explaining the relevant categories of data, purposes, disclosures, rights and contact methods.
- Confirmation and access: to confirm whether your personal data is processed and obtain access to it, subject to applicable protection of trade secrets and other lawful limitations.
- Correction: to request correction of inaccurate personal data, taking account of the nature of the information and the purposes of processing.
- Deletion: to request deletion of personal data concerning you, subject to lawful retention requirements and applicable exceptions.
- Portability: to obtain a copy in a portable and, where technically feasible, readily usable format that permits transmission to another entity without hindrance.
- Opt-out: to stop covered processing for targeted advertising, sales of personal data and profiling used for decisions producing legal or similarly significant effects.
- Withdrawal of consent: to withdraw a consent on which processing depends through an effective method that is at least as easy as the method used to give it.
- Appeal: to challenge a refusal to act on a privacy request through the procedure described below.
- Protection against unlawful discrimination: to exercise statutory rights without retaliation or a service disadvantage prohibited by law.
Rights arising under other applicable statutes remain available. A request does not require the creation of information that we do not hold or the re-identification of qualifying de-identified data.
Your right to opt out
You may exercise an applicable opt-out right by emailing [email protected] and identifying the choice you wish to make. You do not need to explain why you object to a covered sale or targeted advertising. Qualifying universal opt-out signals must be honored for the processing to which they apply. A general browser "Do Not Track" setting is not necessarily the same as a qualifying universal opt-out mechanism. Where an authorized agent submits an opt-out request, we may take reasonable steps permitted by law to verify the agent’s authority. An opt-out does not necessarily prevent processing needed to supply a requested service, maintain security or comply with a legal obligation. It must nevertheless stop the covered processing and must not be circumvented by relabeling its purpose. Any legally permitted incentive or different service connected with data use must be clearly explained and must satisfy the applicable statutory conditions.
Requests concerning journalism and published material
Requests concerning an article, photograph, recording or editorial record are assessed in the relevant legal and factual context. Please identify the material and the correction, deletion or other action sought so that it can be located. Applicable considerations include freedom of speech and the press, privacy, accuracy, source confidentiality, evidentiary privileges and any specific legal restriction. The statutory exclusion for qualifying publicly available information is distinct from constitutional protection for publication. An unfavorable or embarrassing report is not automatically subject to deletion, and prior publication does not automatically justify every subsequent use of the information. Depending on the circumstances, a correction, update, qualification, anonymization or restriction of access may be appropriate. Requests for confidential source information or the identity of an anonymous contributor remain subject to the applicable privileges and procedural safeguards.
How to exercise your rights and response periods
Requests may be sent to [email protected] or the controller’s correspondence address above. No special wording or citation to legislation is required. We may request information reasonably necessary to authenticate an access, correction or deletion request and protect the information of other persons. A complete identity document is not automatically required, and a new account will not be required solely to exercise a right. Under N.J.S.A. 56:8-166.7, covered requests must generally receive a response within 45 days of receipt. An additional 45 days may be used where reasonably necessary because of complexity or the number of requests, with notice and reasons within the initial period. The statutory free-response entitlement applies once per consumer during a 12-month period. Any fee or refusal based on a request being manifestly unfounded, excessive or repetitive must satisfy the statutory conditions; no automatic fee arises merely because a person contacts us again.
Access, verification and reasons for decisions
Access and other requests must be handled in a manner that protects the requester’s information and the lawful rights of others. Where verification is necessary, it must be proportionate to the information and risk involved. New Jersey law does not require authentication of an opt-out request; a refusal based on suspected fraud requires a good-faith, reasonable and documented basis and an explanation to the requester. Where a request is declined, the response must explain the justification and how to appeal. An appeal may be submitted to [email protected] by identifying the earlier request and explaining that you wish to challenge the decision. We will communicate the outcome and reasons in writing within 45 days after receipt of the appeal. If the appeal is denied, the response will explain how to contact the New Jersey Division of Consumer Affairs to submit a complaint.
Privacy complaints and the competent authorities
You may complain directly to us using the privacy contact above. Complaints will be considered without using the complaint process to delay an independently applicable rights-request deadline. The New Jersey Data Privacy Law is enforced by the New Jersey Attorney General through the relevant state authorities. Consumers may report suspected violations to the New Jersey Division of Consumer Affairs. Matters involving federal consumer-protection or children’s privacy requirements may also be reported to the Federal Trade Commission. This Policy does not require permission from us before contacting an authority.
New Jersey Division of Consumer Affairs
124 Halsey Street
Newark, New Jersey 07102
United States of America
Telephone: +1 973 504 6200.
Toll-free within New Jersey: +1 800 242 5846.
Privacy contact and responsibility
The privacy contact for the processing described in this Policy is [email protected]. Requests should identify the relevant service or issue and include sufficient contact information for a response. SCANDIC TRUST GROUP LLC remains responsible for the obligations arising from its controller role. Assigning technical or administrative tasks to another company does not remove that responsibility. Where another organization acts independently, its own responsibilities must be considered according to the processing concerned. This contact point may be used for privacy inquiries, consent withdrawals, statutory requests, appeals and complaints.
J) Security and personal data breaches
Personal data must be protected by reasonable administrative, technical and physical measures appropriate to its nature, volume, use and foreseeable risks. Relevant measures include appropriate access restrictions, confidentiality controls, secure authentication, maintenance, recovery arrangements and protection of data during storage and transmission. No system can guarantee prevention of every incident. Where N.J.S.A. 56:8-163 requires notification, affected New Jersey residents must be notified as expediently as possible and without unreasonable delay, subject to the permitted investigative, restoration and law-enforcement considerations. The required report to the New Jersey State Police must precede notification to affected customers. A processor or other business holding covered records for another organization must provide the notice required by law immediately following discovery. Other statutory notifications must also be made where applicable. A conclusion that notification is unnecessary because misuse is not reasonably possible must satisfy the statutory requirements, including the required written record and retention period.
Risk assessment and responsible use of technology
Where the New Jersey Data Privacy Law requires a data protection assessment for processing presenting a heightened risk of harm, that assessment must be completed and documented before the covered processing takes place. Relevant activities include processing sensitive data, selling personal data and certain targeted-advertising or profiling activities. The assessment must consider the expected benefits, reasonably foreseeable harms, consumer expectations, the context of the processing and available safeguards. A supplier’s description of a service as anonymous, secure or compliant does not determine the legality of its actual use. Processing involving children, precise location, private communications or significant decisions requires consideration of the particular information and risks involved.
K) Disputes, judicial remedies and compensation
This Policy does not restrict access to a competent public authority or court, impose compulsory arbitration or waive a remedy available under applicable law. The New Jersey Data Privacy Law does not itself create a private right of action; enforcement is assigned to the State Attorney General. That limitation does not extinguish an independently available claim under another statute, contract or applicable common law. Potential remedies depend on the legal basis, the facts, the injury and the requirements of the relevant court. A statutory violation does not automatically establish a right to a particular monetary award. In federal court, the constitutional standing requirements addressed in TransUnion LLC v. Ramirez remain applicable, including the requirement for a concrete injury; qualifying intangible injuries can satisfy that requirement. Internal correspondence or settlement discussions do not automatically suspend a limitation period.
L) Relevant legislation and case law
The following legislation and decisions inform the processing and protections described in this Policy. Each applies according to its scope, the facts and subsequent legal developments.
- The New Jersey Data Privacy Law, N.J.S.A. 56:8-166.4 et seq.: governs covered processing, privacy notices, consumer rights, opt-outs, consent, sensitive data, security and the respective obligations of controllers and processors.
- P.L. 2026, c.25: amends the New Jersey privacy framework and introduces additional provisions concerning sensitive-data sales, data brokers and data collectors. The sensitive-data restrictions must be distinguished from registration requirements with a later operative timetable.
- The New Jersey Consumer Fraud Act, N.J.S.A. 56:8-1 et seq., and section 5 of the Federal Trade Commission Act, 15 U.S.C. § 45: address applicable unfair or deceptive commercial practices, including misleading privacy representations and unlawful data practices.
- New Jersey’s secure-disposal and breach-notification provisions, including N.J.S.A. 56:8-162 and 56:8-163: govern disposal of covered records and the notifications required following qualifying security breaches.
- The Children’s Online Privacy Protection Act, 15 U.S.C. §§ 6501–6506, and the Children’s Online Privacy Protection Rule, 16 C.F.R. Part 312, as amended: govern covered collection, use and disclosure of children’s personal information, including parental consent, security and retention.
- The Video Privacy Protection Act, 18 U.S.C. § 2710: restricts specified disclosures of identifiable video-consumption information and establishes particular consent, retention and remedy provisions within its scope.
- The federal Wiretap Act, 18 U.S.C. §§ 2510–2523, the Stored Communications Act, 18 U.S.C. §§ 2701–2713, and the New Jersey Wiretapping and Electronic Surveillance Control Act, N.J.S.A. 2A:156A-1 et seq.: regulate relevant interception, access, use and disclosure of communications, subject to their respective requirements and exceptions.
- The CAN-SPAM Act, 15 U.S.C. § 7701 et seq., and the Telephone Consumer Protection Act, 47 U.S.C. § 227, with applicable regulations: govern commercial email and covered telephone or text communications.
- The First Amendment to the United States Constitution and Article I, paragraph 6 of the New Jersey Constitution: protect freedom of speech and the press and inform the treatment of journalistic publication.
- New Jersey’s newsperson’s privilege, N.J.S.A. 2A:84A-21 et seq., and the federal Privacy Protection Act of 1980, 42 U.S.C. § 2000aa et seq.: provide distinct protections for qualifying journalistic sources, information, work product and documentary material.
- Federal Trade Commission v. Wyndham Worldwide Corp., 799 F.3d 236 (3d Cir. 2015): confirms the Federal Trade Commission’s authority to challenge qualifying cybersecurity practices under the unfairness provisions of section 5. The decision does not impose automatic liability whenever a breach occurs.
- In re Nickelodeon Consumer Privacy Litigation, 827 F.3d 262 (3d Cir. 2016): addresses identifiable video information and New Jersey intrusion-upon-seclusion claims arising from tracking practices and privacy representations. Its treatment of particular identifiers does not establish that all device or browsing information is legally anonymous.
- Dendrite International, Inc. v. Doe No. 3, 342 N.J. Super. 134 (App. Div. 2001): establishes safeguards for applications to compel disclosure of an anonymous online speaker’s identity, including notice, evidentiary requirements and consideration of the competing interests.
- Too Much Media, LLC v. Hale, 206 N.J. 209 (2011): explains that New Jersey’s newsperson’s privilege can extend beyond traditional media, while requiring satisfaction of the statutory connection to qualifying news media and news-gathering activity.
- Cox Broadcasting Corp. v. Cohn, 420 U.S. 469 (1975): protects truthful reporting of information obtained from judicial records open to public inspection in the circumstances addressed by the Court.
- Bartnicki v. Vopper, 532 U.S. 514 (2001): protects publication of information on a matter of public concern in the particular circumstances where the publisher did not participate in the unlawful interception and lawfully obtained the material. It does not authorize unlawful interception or establish unrestricted protection for publication of private communications.
- TransUnion LLC v. Ramirez, 594 U.S. 413 (2021): addresses concrete injury and Article III standing in federal court, including the distinction between a statutory violation and an injury sufficient to support a damages action.
- The Protecting Americans’ Data from Foreign Adversaries Act of 2024, enacted in Public Law 118-50, and the Department of Justice’s Data Security Program under 28 C.F.R. Part 202: impose distinct restrictions on specified sensitive-data transactions within their respective scope.
- Applicable tax and accounting provisions, including 26 U.S.C. § 6001, 26 C.F.R. § 1.6001-1 and N.J.S.A. 54:32B-16: govern preservation of relevant records where the company, transaction and information fall within those requirements.
M) Additional information about particular services
Newsletters and electronic marketing
Where newsletters or promotional communications are offered, the subscription process must explain their nature and the information used to deliver them. Commercial email must comply with the CAN-SPAM Act, including accurate sender information, nondeceptive subject lines, required advertising identification, a valid postal address and a clear method of stopping further marketing. Opt-out requests must be honored within 10 business days. The opt-out mechanism must remain available for at least 30 days after the message is sent, and users must not be charged a fee or required to provide unnecessary information. A newsletter subscription does not authorize unrelated third-party marketing. You may unsubscribe through the mechanism in the message or by contacting [email protected]. Any covered promotional telephone calls or text messages require compliance with the applicable consent and revocation rules.
Newsletter measurement and service messages
Newsletter measurement may involve information about delivery, opening or use of links. An opening pixel or individually identifiable link can disclose information beyond the fact that a message was delivered. Such processing must be explained and assessed according to the information, purposes, recipients and applicable privacy choices. Subscribing to a newsletter does not provide unrestricted permission to combine reading activity with unrelated profiles or disclose sensitive interests. Necessary messages about an account, payment, security incident or service request must remain limited to their purpose. A promotional message does not become exempt from marketing requirements merely because the recipient has an account. Subscription records are retained while needed for the requested communications, followed by the limited retention and suppression arrangements in section H.
Embedded content, social networks and affiliate links
Embedded video, audio, images, social functions and other external resources may disclose IP addresses, device information, the page visited and interaction details to their providers. Disclosure may occur without a platform account, while being signed in may allow the provider to connect the activity with an account. Where consent is required, the relevant processing must not begin before valid consent is obtained. Where an opt-out applies, the affected processing must respect it. The legal treatment of information exchanged through an advertising or affiliate arrangement depends on the actual disclosure and use. Receiving a commission does not itself authorize tracking. Our responsibility for processing that we determine or initiate is not removed merely because another organization receives the information.
YouTube and external video resources
Where YouTube or another video service is embedded, the player and an externally hosted preview image may initiate separate connections to the provider. A preview image may disclose technical information before playback begins. Activating a player may involve further requests, cookies, browser storage or account-related processing, depending on the configuration and settings. A privacy-enhanced mode does not necessarily eliminate every disclosure. Where the Video Privacy Protection Act applies, disclosure of information identifying a consumer’s use of particular video material must satisfy a statutory permission. If consent is relied upon, it must meet the Act’s separate informed-consent requirements; advance consent cannot exceed two years and must be capable of withdrawal as prescribed by the statute. General acceptance of this Policy or an ordinary advertising preference is not automatically sufficient.
Examples of Google cookie durations
Google’s published information describes the following examples. Actual use depends on the service, configuration, location and account settings.
- "YSC": associated with session security and ordinarily retained for the browsing session.
- "__Secure-YNID": used for YouTube functionality and troubleshooting, with a stated duration of six months; Google identifies it as replacing "VISITOR_INFO1_LIVE".
- "PREF": stores playback or display preferences and expires eight months after the user’s last use.
- "SOCS": remembers Google cookie choices, with a stated duration of 13 months.
A cookie’s expiry is different from the retention period for information already transmitted to a provider. These examples do not establish that every listed cookie is placed through our services. A technical description of a cookie does not determine whether its actual use requires consent, is subject to an opt-out or involves another legal restriction.
Profiling and automated decisions
Personalization can involve evaluating identifiers, viewed content and interactions to infer interests or preferences. This may constitute profiling even when it does not produce a legally or similarly significant decision. Under the New Jersey Data Privacy Law, the relevant significant-effect categories include specified decisions concerning financial or lending services, housing, insurance, education, criminal justice, employment, health care and access to essential goods or services. Ordinary article recommendations do not automatically fall within those categories. Where covered significant-effect profiling takes place, the applicable opt-out, transparency, sensitive-data and assessment requirements must be satisfied. A recommendation or inference about an individual must not be treated as unrestricted information merely because it was generated automatically. General acceptance of this Policy does not waive an applicable right concerning automated processing.
Children and young people
Children’s information requires additional protection. The Children’s Online Privacy Protection Act applies to covered child-directed online services and to relevant operators with actual knowledge that they collect personal information from children under 13. Where it applies, parental notice and verifiable parental consent are required before collection, use or disclosure unless a specific exception is available. The amended COPPA Rule also requires separate verifiable parental consent for covered disclosures to third parties that are not integral to the service, including relevant advertising disclosures. Parents have the applicable rights to review information, request deletion and refuse further collection or use. Children’s information must not be retained indefinitely or collected beyond what is reasonably necessary for the activity. Under New Jersey law, covered controllers with actual knowledge, or willful disregard, that a consumer is at least 13 but younger than 17 must obtain the consumer’s consent before targeted advertising, a sale of personal data or profiling for legally or similarly significant decisions. The sensitive-data sales prohibition remains independently applicable. These requirements do not establish a general minimum age for reading publicly accessible news. Any age-verification process must itself be proportionate and protect the information collected.
Events, competitions, photographs and access control
Where events, competitions, reservations or controlled access are offered, the information collected and its purposes must be explained in connection with the activity. Relevant information may include contact details, eligibility information, booking records and necessary access information. Participation does not automatically include consent to unrelated marketing. Photography, filming and security monitoring must comply with applicable privacy, recording and publicity-rights requirements. Attendance alone does not provide unrestricted permission for every future promotional use of a person’s image. Information about children and sensitive circumstances requires particular care. Identity documents, dates of birth or financial details must be requested only where justified by the actual purpose. Security footage must be retained for an appropriate period and deleted earlier than the general maximum in section H where continued retention is unnecessary.
Changes to this Privacy Policy
This Policy may be updated to reflect changes in the services, processing activities or applicable law. Material changes will be communicated in a manner appropriate to their significance, including a notice within the affected service or a direct communication where appropriate. The revised text will identify its effective date. Before personal data is used for a materially different purpose, the applicable information and purpose-limitation requirements must be satisfied and fresh consent obtained where required. Publication of a revised Policy, silence or continued use does not constitute consent to new processing or retrospectively authorize an earlier unlawful activity. An existing opt-out or consent withdrawal remains effective unless it is validly changed. The date below identifies the latest revision of this text.
Contact:
"AMERICAN MARCONI WIRELESS NEWS"
Email: [email protected]
© 2026 "AMERICAN MARCONI WIRELESS NEWS" - All rights reserved, subject to statutory exceptions.
Last updated: November 1, 2026.