jQuery Versions Linked to Known Security Flaws Detected On 40 Of 84 Japanese Websites Scanned
 Hamilton takes record 105th pole and first for Ferrari, as Antonelli lurks
 German rioters loot shops as 'Gen Z' demos turn ugly
 Barca hammer Alaves to retain Liga top spot
 UK king to address Commonwealth with 'unflinching honesty' amid slavery focus
 US judge dismisses Trump lawsuit against Wall Steet Journal over Epstein letter
 Polish president holds crisis talks in court standoff
 NFL to review new allegations against Packers' Jacobs: reports
 Le Havre owners sack coach after PSG thrashing
 De Minaur upsets Zverev and will face Alacaraz in Vienna final
 German police, protesters clash after 'Gen Z' demos
 Fresh frustration for Maresca as Man City lose to Brighton
 Norris fastest ahead of Antonelli in final Mexico practice
 Hammers boss Nuno under pressure after West Brom loss
 'Trump betrayed us': Arizona's Latino voters sour on president
 Fresh anti-government protest flares in Albania's capital
 Clashes break out as hundreds of thousands protest in France
 German police fire water cannon during tense 'Gen Z' protests
 Forced to eat grass, Oleshky evacuees say truce was a 'blessing'
 UK police arrest Palestine Action supporters ahead of Supreme Court hearing
 Harmer and Rabada wrap up South Africa series win over Australia
 Senegal kicks off Youth Games, Africa's first ever Olympics
 Russia says responding to US report of planned attack on Moscow
 Carrick expects Man Utd stay despite Chelsea defeat
 China state TV does not air first La Liga games since Mbappe furore
 Thousands turn up for France protests amid tight security
Fixes released in 2020; Spider Labs urges checks to address potential data-leak risks
TOKYO, JP / ACCESS Newswire / October 29, 2026 / Spider Labs, Inc. (headquartered in Minato-ku, Tokyo; CEO: Satoko Otsuki) detected jQuery versions associated with known security flaws on 40 of 84 Japanese websites (47.6%) scanned with Spider AF SiteScan. The associated flaws could lead to data leakage if exploitation conditions are met. jQuery is a software library that supports website displays and interactions, and fixes for the issues were released in April 2020. As the Information-technology Promotion Agency, Japan (IPA), calls for security checks, Spider Labs is urging website teams to work with their developers and maintenance providers to review their sites. Its existing free scan can help teams assess their current security posture.
Rising data-breach reports prompt calls for security checks
According to a survey published by MM Research Institute on October 14, 454 cyberattack-related data-leak incidents, including potential leaks, were publicly reported in Japan from January through September 2026, up 49% year over year. [1] On October 9, IPA urged organizations to check for unapplied patches in the components of internet-facing applications. [2]
jQuery versions linked to known security flaws detected on 40 sites
The sample comprised 84 Japanese websites across sectors including finance, real estate, retail and e-commerce. jQuery is a "library"-a collection of code that supports website displays and interactions. On 40 sites, SiteScan detected versions associated with known vulnerabilities, or weaknesses in software, identified as CVE-2020-11022 and CVE-2020-11023. These issues were fixed in jQuery 3.5.0, released in April 2020. No official fixes were released for the 1.x or 2.x branches; using an official fixed release requires migration to 3.5.0 or later. [3]
When a website processes attacker-controlled content through certain jQuery functions, these issues can allow malicious code to run in a visitor's browser. [3] As a general effect of cross-site scripting (XSS), attackers could read form entries and send them to an external destination, depending on how a site is built and what information the code can access. [4] Developers and maintenance providers need to examine how the library is used and what protections are in place to assess the impact on a particular site.
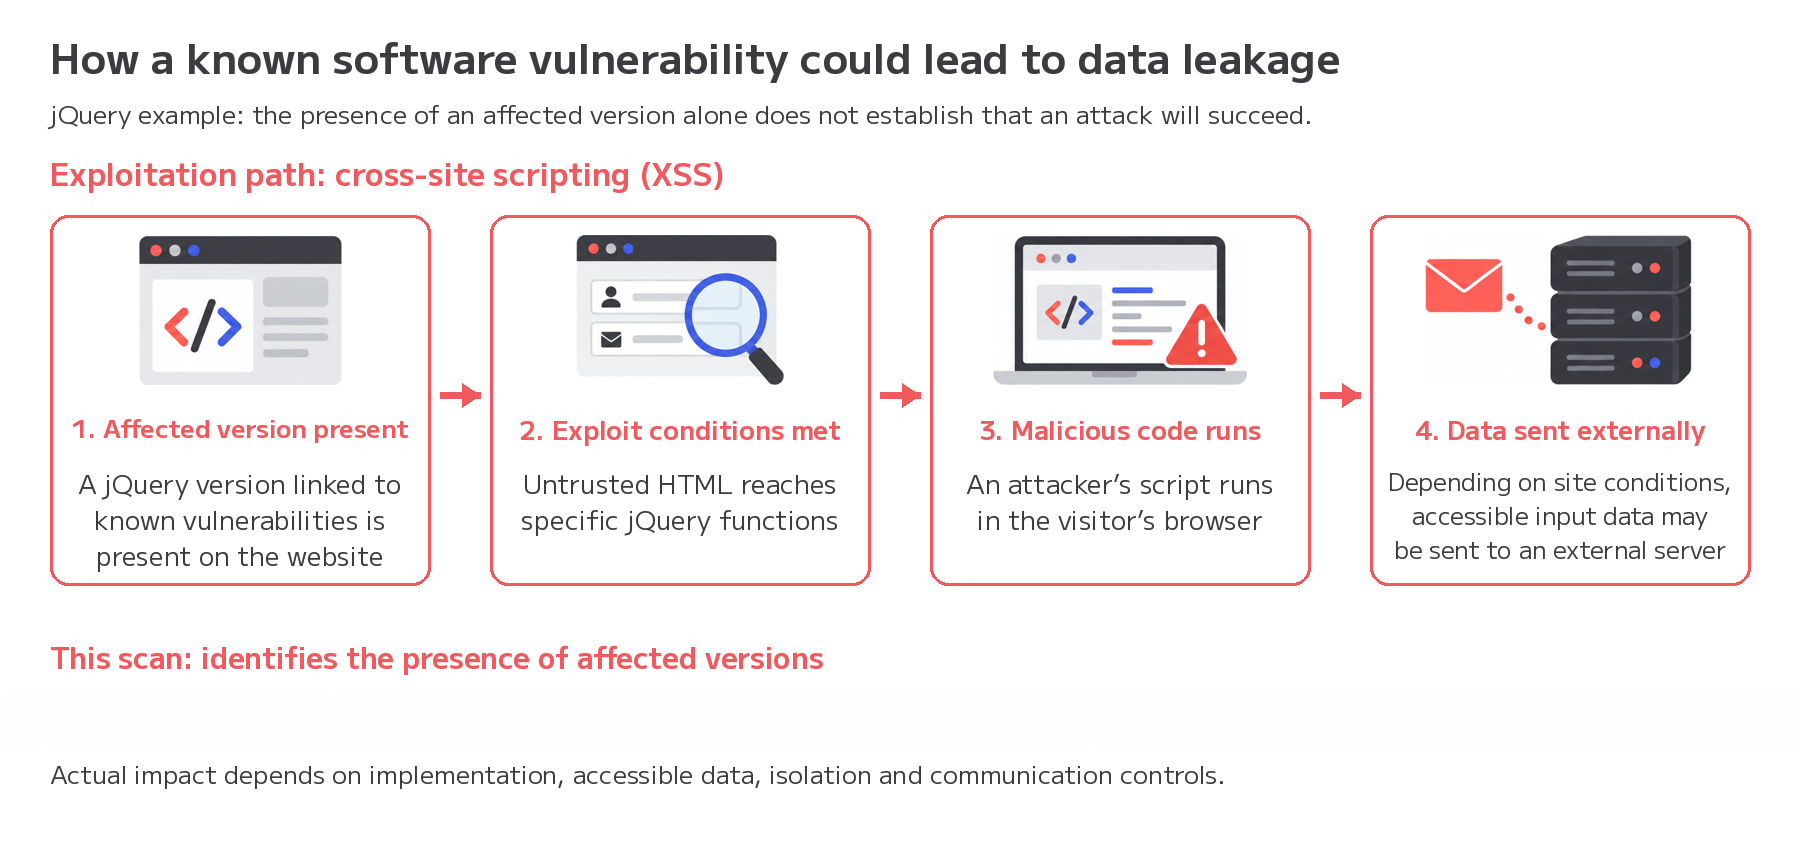
Across the 84-site sample, 56 sites (66.7%) had library or script versions associated with known vulnerabilities. XSS-related findings were the most common, appearing on 51 sites (60.7% of the full sample), including the 40 sites with the jQuery findings described above. Other findings involved prototype pollution, which can affect program behavior, and regular expression denial of service (ReDoS), which can cause processing delays or stoppages.
The diagram combines the jQuery issues with general XSS effects. Sources: [3], jQuery's security advisories; [4], OWASP.
[3] jQuery security advisory / [4] OWASP: Cross Site Scripting
Review updates and responsibilities before a breach occurs
The absence of a breach does not establish that a software issue has been resolved. Even when a website looks and works normally, weaknesses that could be exploited may remain. Reviewing the code in use and the protections in place is an important step before damage becomes visible.
When updating website content, teams should also check updates to the code that keeps the site running. Even where development is outsourced, organizations should clarify who handles security after launch. Spider Labs recommends the following three steps. [5]
| 1. Identify the code in use | Work with developers and maintenance providers to list the libraries and third-party tags in use, their versions, and the pages that use them. Include older pages and legacy files that are still in use. |
| 2. Assess impact and action | Ask whether the findings apply to how the website uses the library and what protections are already in place. Before updating, assess possible effects on forms and checkout functions. |
| 3. Update and maintain | Define who handles security updates and what maintenance covers. Apply necessary updates, test the site and rescan. Establish ongoing checks and updates after launch. |
Methodology and notes
Sample: 84 Japanese websites scanned through sales demonstrations, trials or similar activities, spanning 66 domains. Some sites belong to the same company. Internal and test sites were excluded.
Collection period: October 7-13, 2026 (seven days).
Industries (approximate company-assigned categories): business services and software, 24; finance, 17; real estate, 12; retail and e-commerce, 10; media, 8; travel, 6; education, 3; other, 4 sites.
Method: Library version numbers were matched against known-vulnerability information, primarily on homepages. Older versions with backported fixes are also detected and counted.
Scope: Library- and script-derived findings. Configuration issues such as cookie settings were excluded from the dataset.
Counting: Categories overlap. The sales-demo and trial sample is not an estimate of prevalence across Japan. Individual websites and companies are not disclosed.
Notes: Verification of exploitability, attacks, data leakage and effects on data-entry pages was outside the study's scope. Time since a fix was released differs from how long each site has used a version. Recent breach reports provide background and concern a separate population from this scan sample.
Interpreting website assessment results
Website assessment results provide a basis for technical review. Developers and maintenance providers can use the findings to examine how affected libraries are used, assess existing protections and determine whether updates or other measures are needed.
About Spider Labs
Spider Labs develops and operates Spider AF, a marketing security SaaS platform that addresses fraud and security risks involving advertising, e-commerce, leads and websites.
Its website security assessment tool, Spider AF SiteScan, includes a free scan that reports JavaScript libraries associated with known vulnerabilities and provides findings and scores for basic security settings, including HTTP security headers.
Product information: https://spideraf.com/sitescan
Headquarters: 4F, Minami-Aoyama ST Building, 7-10-3 Minami-Aoyama, Minato-ku, Tokyo, Japan. CEO: Satoko Otsuki.
Established: April 2011.
Website: https://spideraf.com/
Media contact: Anju Morita, Public Relations, Spider Labs, Inc.
Email: [email protected] | Tel: +81-3-6419-7946
Sources.
[1] MM Research Institute: Survey of cyberattack-related data leaks in Japan, October 14, 2026.
[2] IPA: Security alert and recommended checks, October 9, 2026.
[3] jQuery 3.5.0 release announcement; CVE-2020-11022 and CVE-2020-11023 developer advisories.
[4] OWASP: Cross Site Scripting (XSS).
[5] OWASP: Vulnerable Dependency Management Cheat Sheet.
SOURCE: Spider Labs, Inc.
View the original press release on ACCESS Newswire
F.Pedersen--AMWN