Meta warns of password stealing phone apps / Photo: Kirill KUDRYAVTSEV - AFP
 Pope Leo begins three-country South American tour in Uruguay
 Khawaja says entire Australia camp knew of 2018 ball-tampering plan
 November Foraging Guide: Edible Mushrooms and Critical Safety Protocols
 Microsoft Updates Xbox PC App with 60% Faster Startup and Redesigned Interface
 Early Polar Vortex Disruption Creates Uncertain Winter Outlook for Pennsylvania
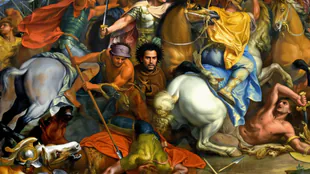 Edmund Richardson Wins Baillie Gifford Prize for 'Alexander' Biography
Meta warned a million Facebook users Friday that they have been "exposed" to seemingly innocuous smartphone applications designed to steal passwords to the social network.
So far this year, Meta has identified more than 400 "malicious" apps tailored for smartphones powered by Apple or Android software and available at the Apple and Google app stores, director of threat disruption David Agranovich said during a briefing.
"These apps were listed on the Google Play Store and Apple's App Store and disguised as photo editors, games, VPN services, business apps and other utilities to trick people into downloading them," Meta said in a blog post.
The apps often ask people to login with their Facebook account information to use promised features, stealing usernames and passwords if entered, according to Meta's security team.
"They are just trying to trick people into entering in their login information in a way that enables hackers to access their accounts," Agranovich said of the apps.
"We will notify one million users that they may have been exposed to these applications; that is not to say they have been compromised."
More than 40 percent of the apps Meta listed involved ways to edit or manipulate images, and some were as seemingly simple as using smartphones as flashlights.
"Our sense is these types of malicious app developers try to target multiple services," Agranovich said, noting the app creators are likely after passwords to more than just Facebook accounts.
"The targeting here seemed to be relatively indiscriminate -- get people to download the applications around the world in an attempt to get access to as many login credentials as possible."
Meta said that it shared what it discovered with Apple and Google, who control what is offered at their respective app shops and each vet offerings.
Apple did not respond to questions regarding whether it took action against any of the apps Meta deemed malicious.
But Google said that most of the apps Meta flagged had already been identified and removed from the Play store by its own vetting systems.
"All of the apps identified in the report are no longer available on Google Play," a spokesperson told AFP.
"Users are also protected by Google Play Protect, which blocks these apps on Android."
M.Fischer--AMWN