-
 Trump names Stephen Miller as White House chief of staff after midterm losses
-
The Good Daughter adapts Karin Slaughter thriller with Rose Byrne and Meghann Fahy
-
 Restored Albanian tower houses anchor new rural tourism trail
-
Heavy-lift drone evacuates wounded Ukrainian soldier from frontline kill zone
-
 Sonia Gandhi reflects on family tragedy and reluctant political career
-
Morrison says West Brom recovered after pressure from successive derby losses
-
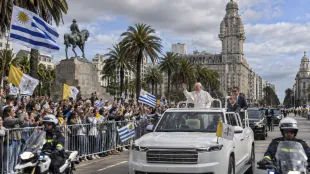 Pope Leo begins three-country South American tour in Uruguay
-
Britain considers 2027 state visit for Ukraine’s Zelensky
-
 Khawaja says entire Australia camp knew of 2018 ball-tampering plan
-
Anna Miltina Confronted with Racism Allegations on ProSieben Show
-
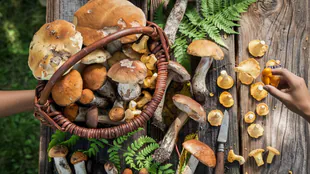 November Foraging Guide: Edible Mushrooms and Critical Safety Protocols
-
German Auto Giants Face Existential Crisis as China Sales Plummet
-
 Microsoft Updates Xbox PC App with 60% Faster Startup and Redesigned Interface
-
Cause of Death Revealed for 'Ellen' Producer Matthew Wright
-
 Early Polar Vortex Disruption Creates Uncertain Winter Outlook for Pennsylvania
-
DEA Marijuana Rescheduling Hearing Closes With Government Not Meeting Its Burden Of Proof?
-
 How to Enjoy Luxury Experiences on a Budget
-
Edmund Richardson Wins Baillie Gifford Prize for 'Alexander' Biography
-
 Pakistan Demands Grant-Based Climate Finance at COP31 to Avoid Debt Trap
Australian insurer warns of 'distressing' hack threat
A major Australian health insurer warned Tuesday of a "distressing" threat by a purported hacker to release client data within 24 hours, following a hack affecting 10 million people.
Medibank Private, one of Australia's largest insurers, told customers to be "vigilant" after the reported threat, issued a day after it had ruled out paying any ransom demand.
The company revealed Monday that a hack originally thought to have breached the data of 3.9 million people had in fact given access to the names, birth dates, addresses, phone numbers and emails of about 9.7 million former and existing clients.
Those numbers included 1.8 million international customers.
On Tuesday, an anonymous poster on a hacking blog -- widely cited by Australian media -- said that data from the Medibank hack "will be publish in 24 hours".
It was not possible to confirm whether the poster was connected to the hack or had access to people's stolen information.
"We knew the publication of data online by the criminal could be a possibility, but the criminal's threat is still a distressing development for our customers," Medibank chief executive David Koczkar said, calling for clients to be "vigilant".
"We unreservedly apologise to our customers," he added.
The hacker could also attempt to contact customers directly, the company warned.
- 'Betrayal' -
Medibank had said in Monday's announcement that it believed "all of the customer data accessed could have been taken by the criminal".
The data breach included some people's health claims along with codes exposing their diagnoses and medical procedures, as well as the passport numbers and the visa details of international students.
Medibank said it was working with the Australian government and with the police, who were trying to prevent the sharing and sale of the stolen data.
Cybercrime experts had advised that paying a ransom had only a "limited chance" of ensuring the return of the stolen data, the company said, explaining its decision to reject any ransom demand.
Two law firms said Tuesday they had joined forces to investigate a possible class action lawsuit against Medibank.
"We believe the data breach is a betrayal of Medibank Private's customers and a breach of the Privacy Act," said a joint statement by Bannister Law and Centennial Lawyers.
"Medibank has a duty to keep this kind of information confidential."
The Medibank hack followed an attack on telecom company Optus in September that exposed the personal information of some nine million Australians.
As data theft becomes more common, it may raise questions over the need for Australian businesses to gather customers' sensitive personal information, said Michael Duffy, associate professor of corporate law at Monash University.
Some of those data retention policies were dictated by government regulation, he added.
"Nevertheless, businesses requesting and keeping personal details that aren't completely essential could become more legally problematic for them, if they are hacked."
Ch.Havering--AMWN